
Nova Scotia Power admits it cannot explain why stolen customer data was not deleted before cyberattack
HALIFAX – Nova Scotia Power officials say they cannot explain why a digital file containing nearly three decades of customer information was not automatically deleted from their systems before it was stolen in a March 2025 cyberattack, a failure that has left hundreds of thousands of ratepayers exposed to potential fraud and identity theft.
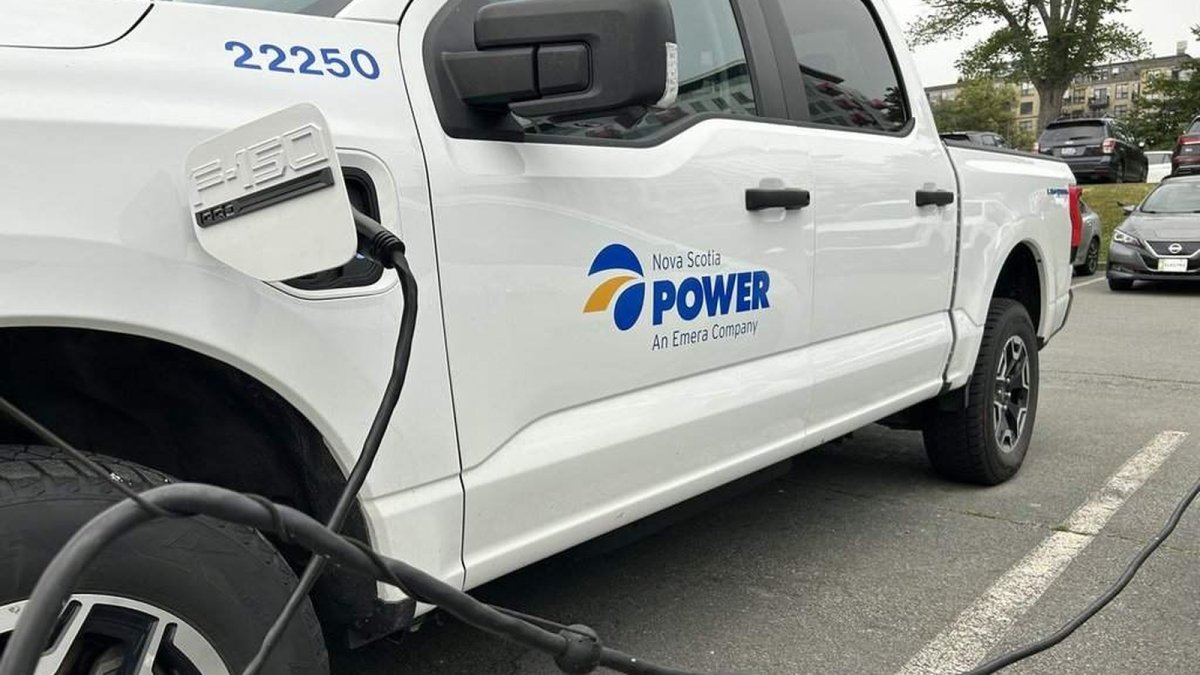
Nova Scotia Power admits it cannot explain why stolen customer data was not deleted before cyberattack
HALIFAX – Nova Scotia Power officials say they cannot explain why a digital file containing nearly three decades of customer information was not automatically deleted from their systems before it was stolen in a March 2025 cyberattack, a failure that has left hundreds of thousands of ratepayers exposed to potential fraud and identity theft.
Blake Williams, an executive with the utility, told a regulatory hearing before the Nova Scotia Utility and Review Board (UARB) that the company has automated mechanisms designed to purge certain categories of data on a cycle of no more than 90 days. However, he acknowledged the utility does not know why a file created in 2021 remained present in the system when attackers accessed it in March 2025.
Tags: Nova Scotia Power, cyberattack, data breach, Blake Williams, UARB, Office of the Privacy Commissioner, Emera, customer data, social insurance numbers, Russia-based actors, critical infrastructure, Atlantic Canada, utility regulation, PIPEDA
The breach: What happened and when
The cyberattack was confirmed in April 2025, with the breach itself discovered on April 25 of that year. Nova Scotia Power, the primary electric utility for the province and a privately owned subsidiary of Emera Inc., serves roughly 500,000 customers across Nova Scotia. The stolen data was later released on the dark web, impacting approximately half of the utility's customer base.
The compromised information included addresses, phone numbers, banking information, social insurance numbers, and other sensitive customer data. The company has said it believes the attackers were Russia-based actors, though specific attribution has not been independently confirmed by Canadian authorities.
Williams' testimony before the UARB marks the first time the utility has publicly addressed the deletion failure in a formal regulatory setting. His admission raises serious questions about the company's data governance practices and whether its internal controls were adequate to protect customer information over an extended period.
The 90-day deletion cycle and the 2021 file
According to Williams, Nova Scotia Power has mechanisms in place to automatically delete certain data in cycles of no more than 90 days. These protocols are designed to limit the amount of sensitive information retained on company systems, reducing both privacy risks and the potential impact of any security breach.
Yet the file in question, created in 2021, was still present in the system when attackers gained access in March 2025. That means the data survived at least four years beyond its intended retention window, and potentially longer depending on when the deletion cycle should have first applied to it.
"We don't know why the file was not deleted as intended," Williams told the hearing, according to testimony reviewed by Global1.News. "If it had been destroyed as intended, the information would not have been available to the attackers."
The executive's admission underscores a critical gap between policy and practice at the utility. While automated deletion mechanisms exist on paper, their implementation appears to have failed in this instance, with no clear explanation for the oversight.
Regulatory and federal scrutiny
The breach has drawn attention from multiple oversight bodies. The Office of the Privacy Commissioner of Canada has been conducting a federal investigation into the customer data theft, examining whether Nova Scotia Power complied with the Personal Information Protection and Electronic Documents Act (PIPEDA), the federal private-sector privacy law.
PIPEDA requires organisations to protect personal information and to retain it only as long as necessary to fulfil legitimate business purposes. If the utility's own deletion policies were not followed, that could constitute a violation of the law's accountability principle, which holds organisations responsible for the personal information under their control.
The UARB hearing represents a separate but parallel avenue of scrutiny. The provincial regulator oversees Nova Scotia Power's operations, including matters of reliability, ratepayer protection, and service quality. The board's interest in the cyberattack reflects broader concerns about how the utility manages risks that could affect customer trust and the stability of essential services.
Federal-provincial jurisdiction over utilities and privacy adds another layer of complexity. While the Privacy Commissioner's office operates at the federal level, the UARB has authority over the utility's provincial operations. Coordinating these investigations requires careful navigation of overlapping mandates, though both bodies appear to be pursuing their respective inquiries.
Impact on customers and the dark web release
The release of the stolen data on the dark web has created lasting risks for affected customers. With banking information and social insurance numbers in the hands of unknown actors, roughly 250,000 Nova Scotians face the possibility of financial fraud, identity theft, and other forms of criminal misuse.
Social insurance numbers are particularly concerning because they are difficult to change and can be used to open credit accounts, file fraudulent tax returns, or obtain government benefits under false pretences. Unlike a credit card number that can be cancelled and reissued, a compromised SIN remains a vulnerability for life.
Nova Scotia Power has said that its business IT networks and customer account access were affected by the breach, but that power grid operations were not compromised. That distinction is important for public safety, but it offers little comfort to customers whose personal financial information is now circulating in criminal forums.
The utility has faced criticism for the timeline of its disclosure. The breach was confirmed in April 2025, but the company has not provided a detailed public accounting of when it first became aware of the intrusion or how quickly it notified affected customers. The UARB hearing may shed further light on these questions as it continues.
Broader implications for Canadian critical infrastructure
The Nova Scotia Power breach is part of a troubling pattern of cyberattacks targeting Canadian critical infrastructure. The Canadian Centre for Cyber Security has repeatedly warned that utilities, telecommunications providers, and other essential services are attractive targets for state-sponsored actors and criminal groups alike.
Electric utilities occupy a unique position in the national security landscape. They are essential to daily life, economic activity, and public safety, yet they also hold vast amounts of personal data about their customers. That combination makes them a high-value target for actors seeking either to disrupt services or to harvest sensitive information.
The fact that the attackers appear to have been Russia-based is consistent with broader trends in cyber espionage and criminal activity. Russian-speaking cybercriminals have been implicated in numerous high-profile breaches of Western organisations, and state-aligned groups have shown interest in Canadian infrastructure.
However, the deletion failure at Nova Scotia Power highlights a vulnerability that is entirely domestic in origin. Even the most sophisticated external defences cannot compensate for internal failures to follow established data management protocols. The company's inability to explain why a file survived beyond its intended deletion window suggests a systemic weakness in its data governance practices.
What happens next
The UARB hearing is expected to continue, with further testimony from Nova Scotia Power officials and potentially from independent experts. The board may issue recommendations or directives aimed at improving the utility's data management and cybersecurity practices.
The Office of the Privacy Commissioner's investigation remains ongoing. Under PIPEDA, the Commissioner can make recommendations, enter into compliance agreements, or, in certain circumstances, pursue enforcement action. The outcomes of that investigation could have implications not only for Nova Scotia Power but for other Canadian organisations that handle sensitive personal data.
For affected customers, the immediate priority is protecting themselves from the consequences of the data release. That may involve monitoring bank accounts, placing fraud alerts on credit files, and being vigilant against phishing attempts that could exploit the stolen information.
Nova Scotia Power has said it is co-operating with investigators and has taken steps to strengthen its security posture since the breach. Whether those steps are sufficient to prevent a recurrence remains an open question, one that the UARB and the Privacy Commissioner will likely continue to examine.
The broader lesson for Canadian utilities and other critical infrastructure operators is clear: data retention policies are only as effective as their implementation. A 90-day deletion cycle means nothing if files are allowed to languish for years without oversight. The Nova Scotia Power case should serve as a wake-up call for organisations across the country that handle sensitive customer information.
As the investigations continue, ratepayers and regulators alike will be watching to see whether the utility can provide a satisfactory explanation for its failure and, more importantly, whether it can demonstrate that such a lapse will not happen again.
By Alex Thompson, Staff Writer
This article was produced with AI-assisted research and editorial support. Reporting is based on sources cited in the article.
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0
Canada Correspondent at Global1.News. Based in Toronto, covering Canadian politics, energy, trade, and US-Canada relations. Provides the Canadian perspective on North American and global affairs.








Comments (0)