
Amidst fears of AI cyberattacks, Satya Nadella says lots of critical infrastructure is ‘unpatchable’
Satya Nadella’s warning at the DealBook Summit that a swath of America’s critical infrastructure is “unpatchable” isn’t just tech‑industry hype – it’s a reality check for anyone running production servers.
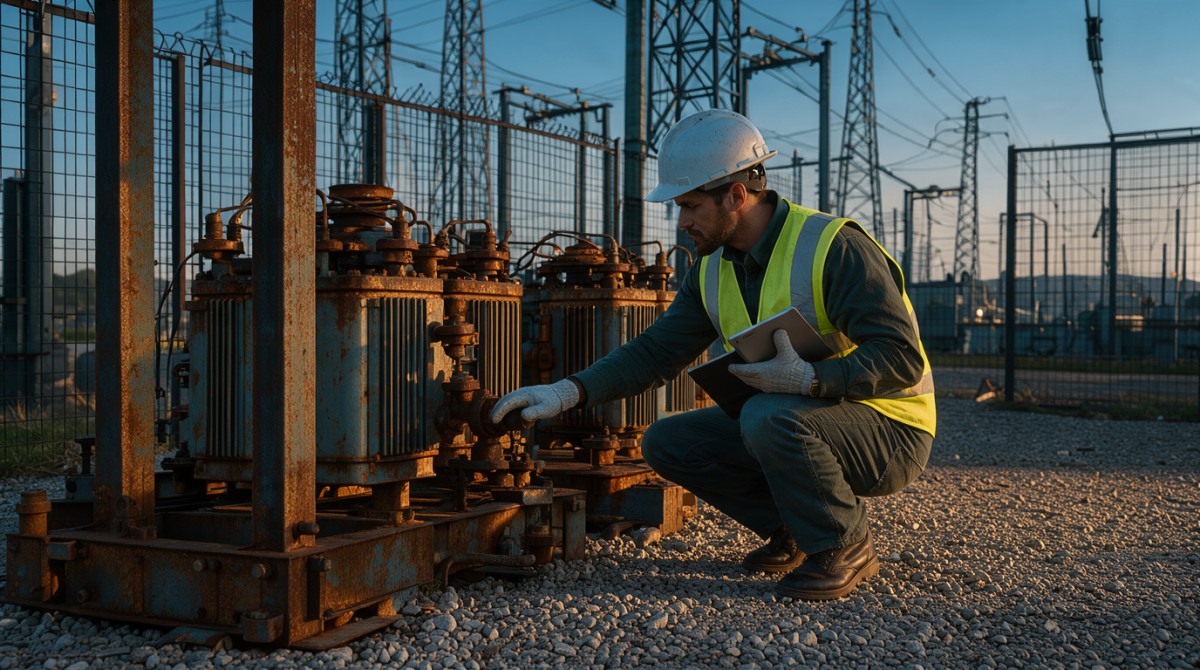
Satya Nadella’s warning at the DealBook Summit that a swath of America’s critical infrastructure is “unpatchable” isn’t just tech‑industry hype – it’s a reality check for anyone running production servers. The Microsoft boss highlighted firmware, chillers and HVAC as examples of everyday hardware that sits on the internet with vulnerabilities that can’t be fixed by a simple software update. In the age of AI‑aided cyber‑attacks, those “dumb” devices become high‑value targets, and the fallout isn’t just a headline; it’s a direct threat to the reliability and cost structure of independent hosting providers.
The AI‑Powered Threat Landscape
Nadella framed the problem as a convergence of two trends: a flood of “latent bugs” that surface in critical systems, and AI tools that dramatically accelerate the discovery and exploitation of those bugs. He noted that the recent Outlook outage was the result of a “latent bug” that created a “perfect storm,” and that similar dynamics are now playing out in transportation, HVAC and other control‑system environments. The implication is clear – AI is no longer a research curiosity; it is a weapon that can turn a minor firmware flaw into a systemic breach in hours.
For hosting operators, the lesson is simple: the same AI‑driven tools that can weaponize firmware bugs can also be turned against our own stacks. If a competitor can weaponize a chillers‑controller firmware flaw, they can equally weaponize a mis‑configured container runtime. The speed at which AI can generate exploit code means the window between discovery and exploitation shrinks to minutes, not days.
Patch Velocity vs. Stability
Nadella warned that the “patch now needs to go instantly from being available to being patched in production, because it’s being exploited in the wild.” That urgency creates a paradox – the faster you push a fix, the higher the risk of destabilizing your environment. In practice, we’ve seen this play out when rushed patches break downstream services, forcing emergency rollbacks and causing downtime that costs customers more than the original vulnerability.
Independent providers have to balance two competing imperatives: rapid response to AI‑driven exploits and maintaining the stability that customers expect. The reality is that many of the “best practices” taught in vendor‑centric webinars – extensive staging, multi‑stage testing, and lengthy change‑approval processes – simply collapse under the pressure of an AI‑generated zero‑day.
Unpatchable Firmware: A Hidden Cost Center
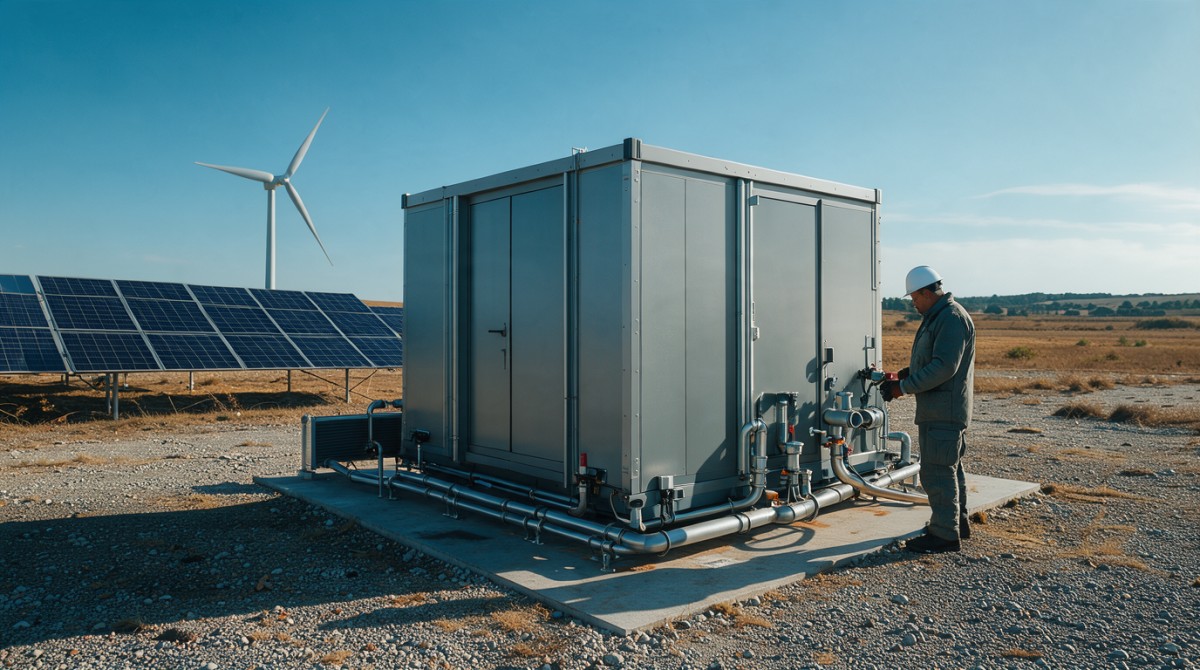
When Nadella pointed to “firmware and the chillers … HVAC systems” as unpatchable, he was highlighting a cost center that most hosting operators overlook. Those devices are often sourced from OEMs that provide no firmware update path, or they run legacy code that cannot be re‑signed without vendor approval. The result is a permanent exposure that can be weaponized by AI tools that can reverse‑engineer firmware binaries at scale.
From a business‑risk perspective, that exposure translates into higher insurance premiums, potential regulatory fines, and the ever‑looming specter of a breach that could force a data‑center shutdown. The prudent move is to inventory every piece of hardware, assess its update capability, and isolate any that cannot be patched behind air‑gapped networks or strict zero‑trust controls.
Real‑World Outages as Warning Signs
The DealBook Summit conversation took place against a backdrop of recent large‑scale outages – Outlook, the NSA, the FFA and Apple – all of which have been speculated to involve cyber‑attacks, though officials deny it. Whether or not AI was the catalyst, the pattern is unmistakable: a single “latent bug” can cascade into a global service disruption.
For us running hosting infrastructure, the takeaway is that a single point of failure in a vendor‑supplied component can ripple across our entire service portfolio. The “perfect storm” Nadella described is not a hypothetical; it’s the same storm that knocked out Outlook for millions of users, and it could knock out a regional data‑center if a critical HVAC controller were compromised.
Why Hyperscalers Aren’t the Safe Harbor They Appear to Be
Nadella’s comments indirectly expose a weakness in the hyperscaler model. While giants like Microsoft can afford massive security teams and rapid patch cycles, they still grapple with unpatchable firmware in their own data‑centers. That reality undermines the narrative that moving to a hyperscaler automatically shields you from these risks.
Independent providers can actually turn this into a competitive advantage by offering tighter control over the hardware stack, transparent firmware policies, and bespoke security hardening. Customers increasingly care about supply‑chain risk, and a provider that can demonstrate a clean, auditable firmware inventory will stand out against the backdrop of “unpatchable” hype.
Actionable Steps for Hosting Operators
First, conduct a comprehensive hardware audit. Identify every piece of firmware‑controlled equipment – from chillers to power distribution units – and document whether a vendor‑provided update path exists. Second, segment any unpatchable devices onto isolated networks with strict access controls; treat them as high‑risk assets and monitor them continuously for anomalous traffic.
Third, build a rapid‑response playbook that balances speed with stability. Pre‑stage patches in a shadow environment, but also define clear rollback criteria to avoid the “instability” Nadella warned about. Fourth, invest in AI‑driven threat‑intelligence that can surface emerging firmware exploits before they hit production. Finally, communicate transparently with customers about the risk profile and the mitigation steps you’re taking – trust is earned by honesty, not by hiding the fact that some devices are “unpatchable.”
Looking Ahead: The Need for a New Security Paradigm
Nadella’s remarks signal that the old patch‑and‑pray model is dead. The industry must move toward a security paradigm that assumes every component – software, firmware, or hardware – could be compromised at any moment. That means designing systems that can survive a breach, not just prevent one.
For independent hosting providers, the path forward is clear: double‑down on hardware visibility, embrace zero‑trust networking, and adopt AI‑assisted monitoring to keep pace with the same AI tools that attackers wield. The era of “unpatchable” infrastructure is here, but it doesn’t have to be a death sentence for our businesses if we act with the same urgency and pragmatism that Nadella demands of the tech giants.
— Allan Ali, Founder
This article was produced with AI-assisted research and editorial support. Reporting is based on the source material cited below. Sources: TechCrunch; techcrunch.com; Global1.News (19 November 2026).
By Allan Ali, Global1.News
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0
Publisher of Global1.News. Automation architect, systems builder, and the guy making sure the truth gets published.









Comments (0)